Capabilities of the appliance
The appliance software consists of nine modules. Seven of them handle security tasks, two provide summary analytics and administration. They all run on a single device and share one view of the network.
- 43 categories of security events4 alert severity levelsPCAP raw traffic export
Traffic monitoring
The appliance inspects a copy of your traffic, matches it against a signature database and raises an alarm when something happens that should not.
Learn moreNetwork activity · Statistics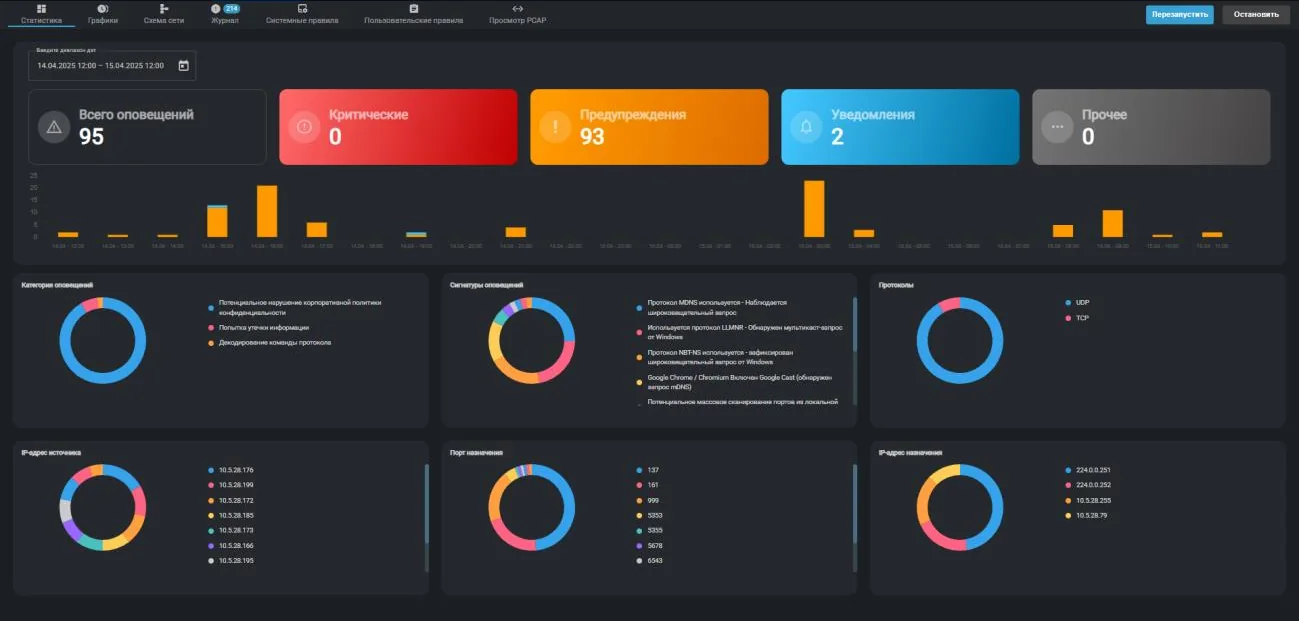
- CVSS severity score for every finding0-100 % quality of detection indicator4 scan types
Vulnerability scanner
The appliance looks for what someone could walk in through: outdated versions, weak algorithms, forgotten services and systems that reached end of life.
Learn moreVulnerability scanner · Log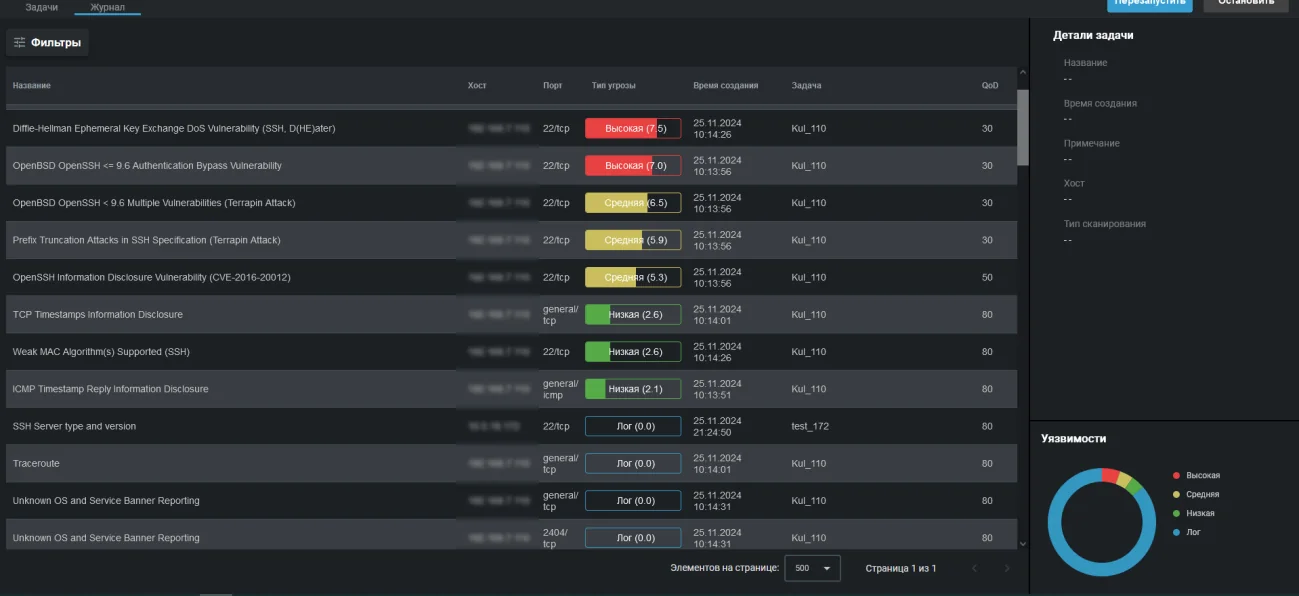
- 65,535 ports in a full TCP scan8 scan profilesCRON arbitrary task schedules
Network inventory
The appliance regularly recounts what lives in your network and reports when the picture changes: a new host appeared, a new port opened, a device went missing.
Learn moreNetwork monitor · Scan result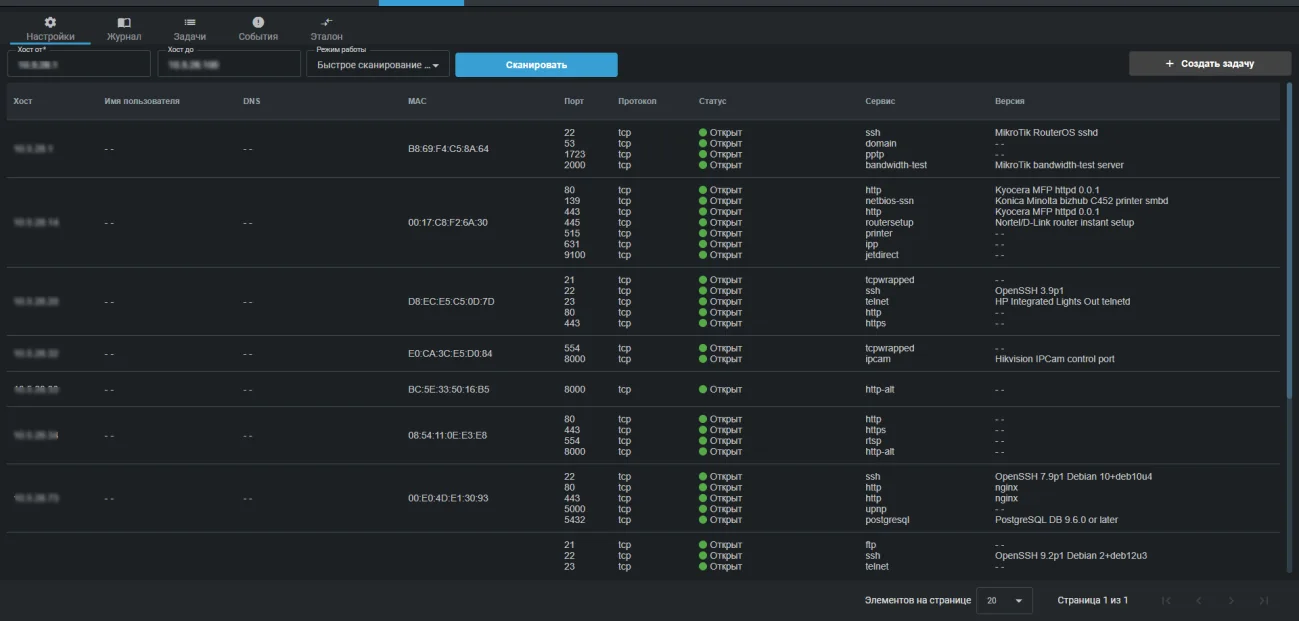
- 10 emulated decoy services2 interaction levels0 false positives by design
Intruder honeypot
The appliance deploys a decoy in your network. A legitimate employee has no reason to touch it, so any request is a signal: somebody is already inside and looking around.
Learn moreVulnerability emulator · Sessions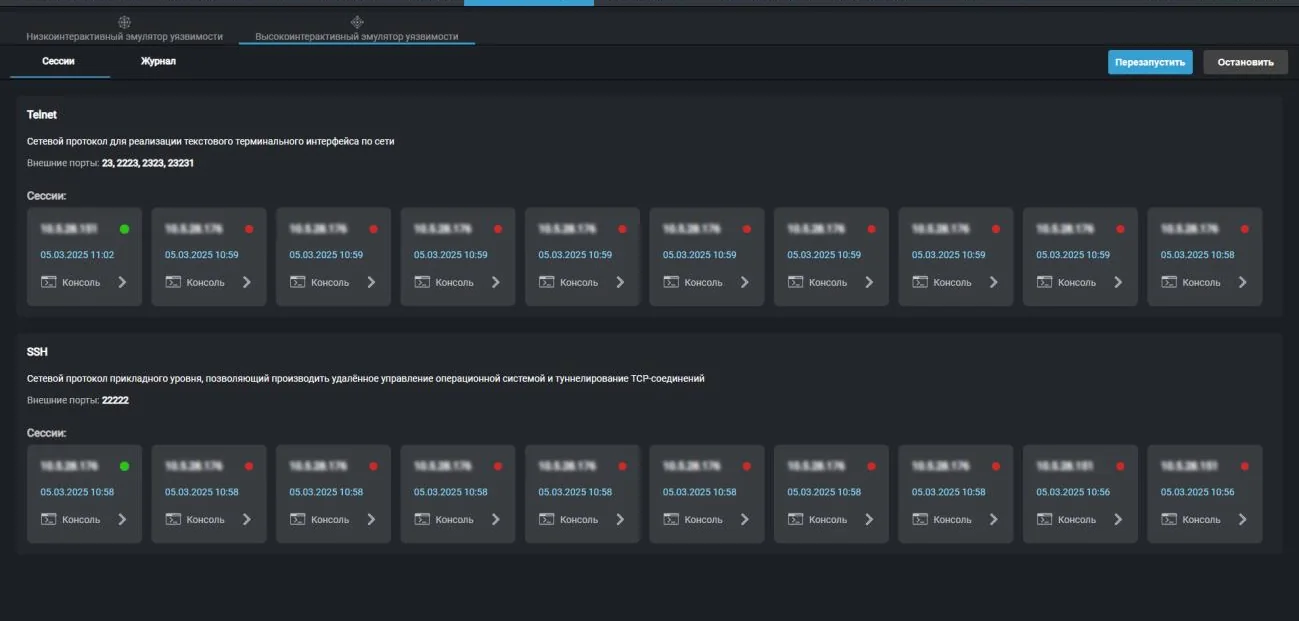
- 2.4 / 5 GHz, both bands802.11 management frame dissectiondBm signal level for every device
Wi-Fi security
You can build a perfect wired perimeter and still have somebody's personal router standing next to the finance department. The appliance listens to the air and shows what is going on.
Learn moreWi-Fi security · Devices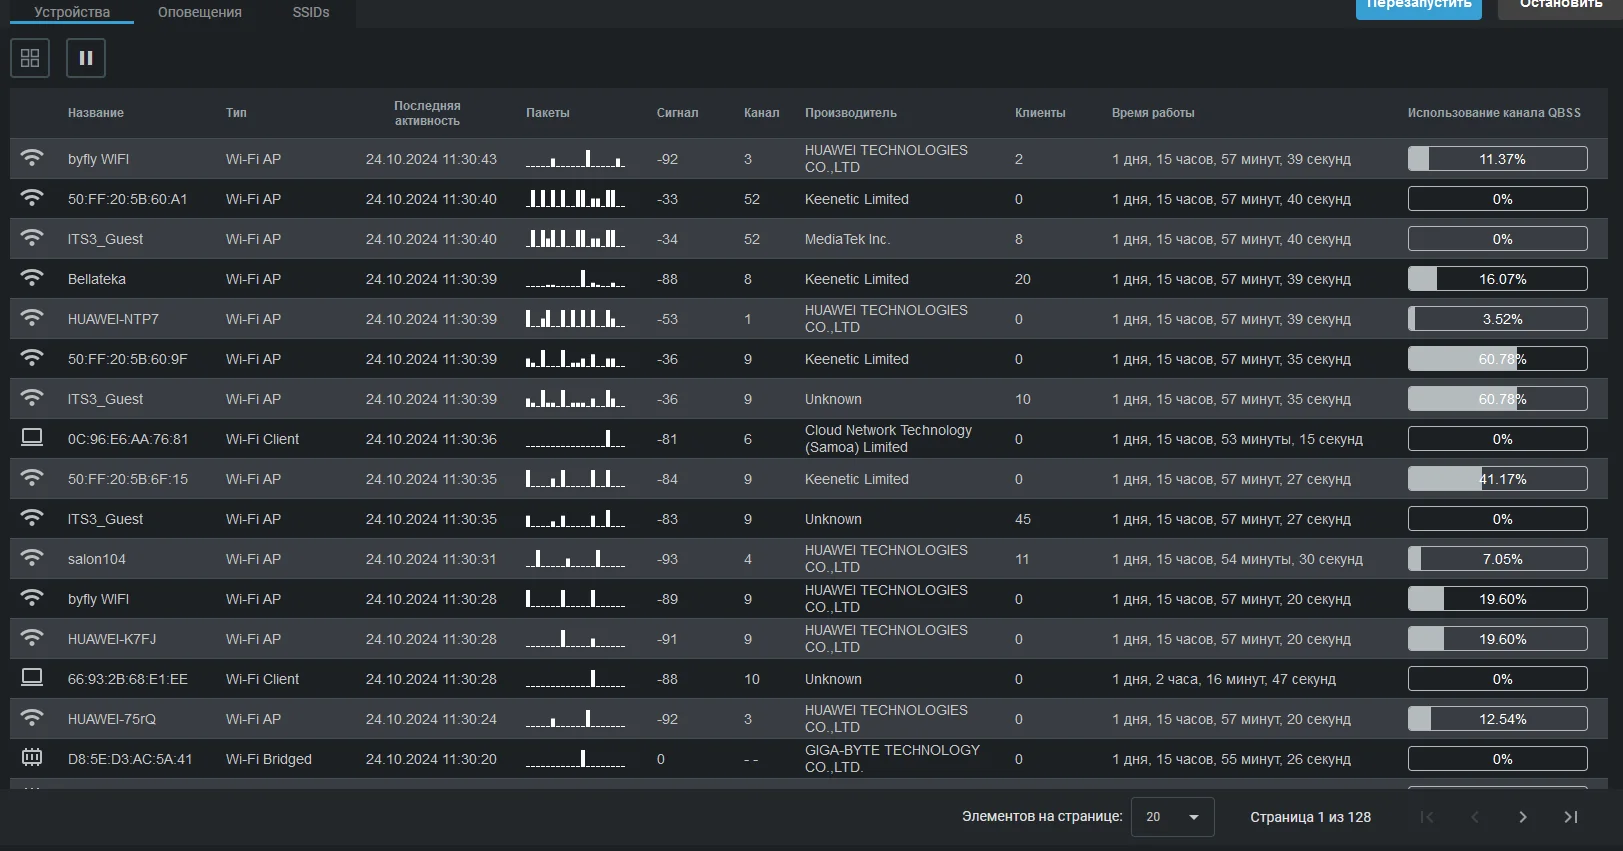
- 4 connection protocols to devices2 control modesSHA content hash comparison
File integrity
A modified router config or a replaced executable on a server generates no suspicious traffic. They are found by comparison against a baseline.
Learn moreInfrastructure integrity · Active connections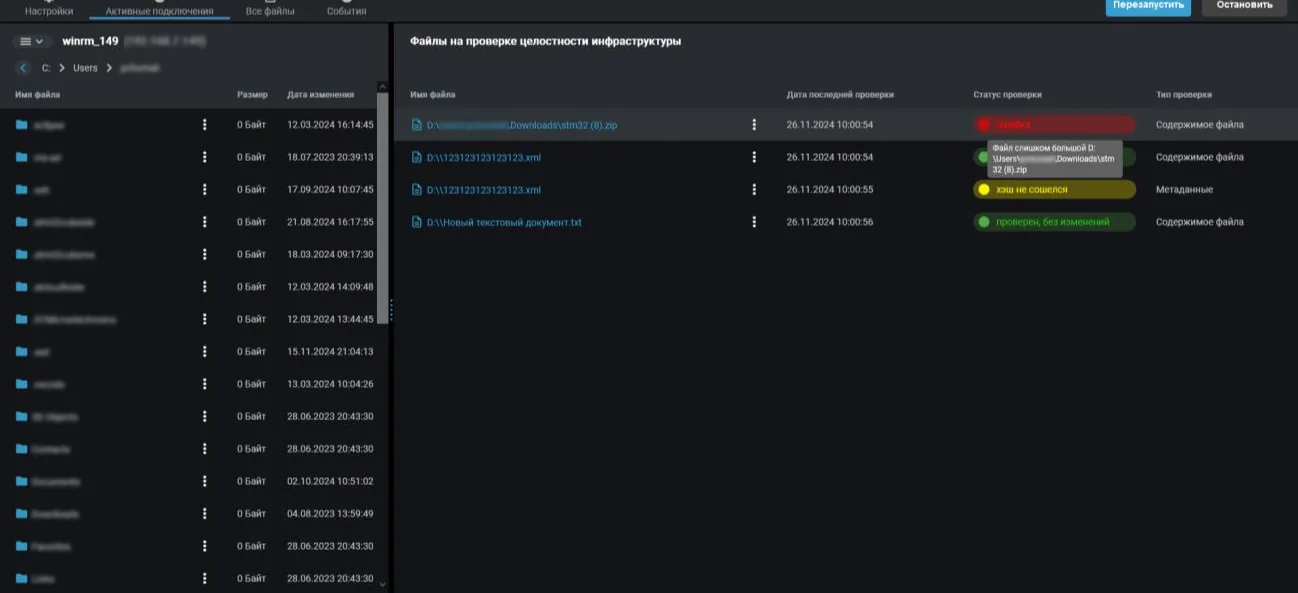
- 514 default syslog port3 report formats5 min minimum notification interval
Reports and SIEM
The appliance does not try to replace your security operations centre. It delivers events where they are already collected, and writes directly to whoever is on duty today.
Learn moreAdministration · Export settings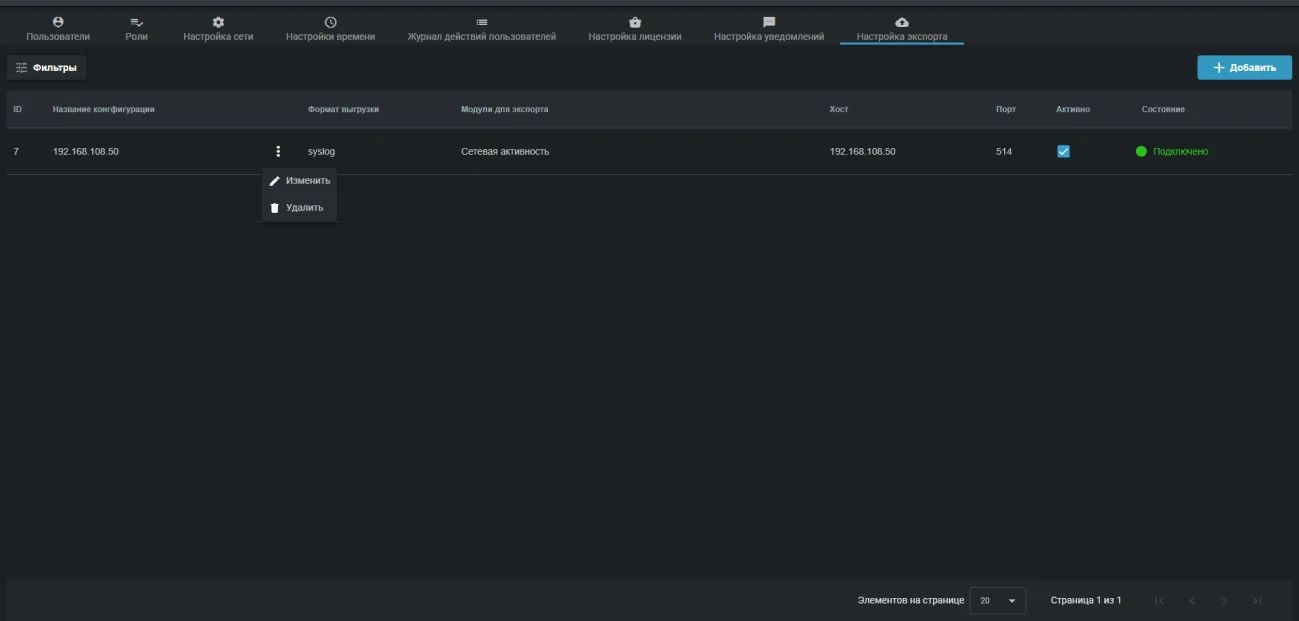
Two service modules that tie the rest together
Analysis
Events from every module over the last 24 hours on one screen, with unread counters and a one click jump into the relevant log. This is the duty operator screen.
Administration
Network, time and NTP, roles and permissions, accounts, user action log, licence, notifications and SIEM export. All in the web interface, no console needed.
We will prepare a quote for your network
Tell us about your infrastructure: how many sites, which switch sits in the core, whether you already run a SIEM. We will pick the edition and the connection scheme, and calculate the cost.
- We reply within one business day
- We design the connection scheme for your topology
- We show the interface on a live demo unit